NewStori...First & Foremost A Quality News Outlet!
Spam email is one of the most persistent problems in modern digital communication. Unwanted messages can range from aggressive marketing and newsletters to phishing attempts, malware campaigns, fraudulent invoices, and messages designed to collect personal information.
One common misconception is that an email coming from a "no-reply" address cannot be traced or responded to.
That is not necessarily true.
A no-reply@example.com address is simply an email address chosen by the sender to discourage recipients from replying. It does not, by itself, reveal who actually operates the sending infrastructure, and it does not necessarily prevent someone from investigating where a message came from.
The important distinction is between replying to the visible sender and identifying the infrastructure that actually delivered the message.
What Does "No-Reply" Actually Mean?
An address such as:
no-reply@example.com
usually means that the organization does not want recipients responding directly to that mailbox.
Sometimes the mailbox genuinely does not accept incoming messages.
In other cases, the address may exist but simply isn't monitored.
A sender can also specify a different address for replies using the email's Reply-To field.
For example:
From: no-reply@example.com
Reply-To: support@example.com
If you press Reply, your email program will normally use the Reply-To address.
This means the visible From address is not necessarily the address that receives responses.
Can You Send an Email Back Anyway?
Technically, an email can be addressed to the visible From address even if it contains the words no-reply.
For example:
To: no-reply@example.com
But that does not mean anyone will receive or read it.
The receiving mail server might:
• Accept the message
• Reject it
• Automatically discard it
• Return a bounce message
• Route it to an unattended mailbox
Therefore, simply replying to a no-reply address is usually not the most effective way to reach the organization responsible for the message.
The More Important Question: Where Did the Email Actually Come From?
Email contains considerably more information than what appears in the visible message.
Most email systems contain headers that provide technical information about how the message was processed.
Depending on the provider and message, headers can contain information such as:
• From
• To
• Reply-To
• Return-Path
• Message-ID
• Received
• Authentication-Results
• SPF results
• DKIM results
• DMARC results
These fields can provide substantially more information than the name displayed in your inbox.
Understanding the "From" Address
The From field is the address most users see.
For example:
From: Billing Department
However, the visible sender information should not automatically be treated as proof that the message originated from that organization.
Email systems can be abused to impersonate legitimate domains.
That is why authentication information is important.
The Reply-To Address
The Reply-To header tells your email application where replies should normally go.
For example:
From: promotions@example.com
Reply-To: marketing@example.com
A reply would normally be directed toward marketing@example.com.
Sometimes this provides a legitimate customer-service address.
Other times, particularly in phishing campaigns, the reply address can be suspicious or unrelated to the apparent sender.
The Return-Path
The Return-Path is associated with the address used for handling delivery failures.
It can be particularly useful when investigating automated email.
For example:
Return-Path:
This may reveal that the organization appearing in the message is using a separate email-delivery service.
That does not automatically mean the message is malicious.
Companies routinely use third-party email providers to distribute legitimate newsletters and transactional messages.
The Received Headers
The Received headers are among the most technically useful pieces of information in an email.
Mail servers generally add these headers as they process a message.
You may see something resembling:
Received: from mail.example.net
by mx.example.org
...
Multiple Received entries can provide a path through which the message traveled.
However, interpreting these headers requires care.
The earliest visible server in the chain is not automatically the physical computer used by the person who created the message.
Modern email systems frequently involve:
• Cloud email providers
• Marketing platforms
• Security gateways
• Forwarding services
• Content filters
• Mailing-list systems
Consequently, the headers should be interpreted as a chain of mail-handling systems rather than as a guaranteed physical location of the sender.
SPF, DKIM, and DMARC
Modern email authentication provides another important source of information.
SPF
Sender Policy Framework (SPF) allows a domain to specify which servers are authorized to send mail on its behalf.
An SPF result might appear as:
spf=pass
or:
spf=fail
An SPF failure can be a warning sign, although it does not automatically prove that an email is malicious.
DKIM
DomainKeys Identified Mail (DKIM) adds a cryptographic signature to an email.
A receiving mail server can verify the signature using information published by the sending domain.
A successful DKIM result can provide evidence that the message was authorized by the domain associated with the signature.
DMARC
Domain-based Message Authentication, Reporting, and Conformance (DMARC) builds on SPF and DKIM.
It allows domain owners to publish policies concerning messages that fail authentication and alignment checks.
Together, these systems make it more difficult for attackers to impersonate legitimate domains successfully.
How to View Full Email Headers
Most major email services provide an option to view the original message or full headers.
The terminology varies.
Look for options such as:
• Show original
• View source
• View message details
• Show headers
• View raw message
Do not confuse the message body with the complete email source.
The full source may contain considerably more technical information.
Can You Send a Message Directly to the Real Source?
Sometimes—but "source" needs to be defined carefully.
If the message comes from a legitimate company, the headers may reveal the company's actual email domain or the third-party service it uses.
You may then be able to contact the organization through an official address listed on its website.
For example, suppose you receive:
From: no-reply@company.example
Reply-To: no-reply@company.example
but the headers indicate that the message was distributed through:
mailer.vendor.example
That does not necessarily mean the vendor is responsible for the content.
The vendor may simply provide infrastructure to the company.
The safest approach is to identify the organization independently rather than blindly emailing every address appearing in the headers.
Don't Automatically Email the Technical Infrastructure
This is an important distinction.
Finding a server or mail-delivery provider does not mean you have found the person responsible for the spam.
A large organization might use an external service to send millions of legitimate messages.
Likewise, a malicious sender might use a compromised account or infrastructure belonging to an innocent third party.
Sending complaints to unrelated technical addresses can therefore create additional problems.
Instead, determine whether the message appears to be:
• Legitimate marketing
• An unwanted commercial message
• Phishing
• Malware
• Fraud
• Account compromise
• Spoofing
• A message sent through a legitimate third-party service
The appropriate reporting channel depends on the category.
Reporting Is Usually Better Than Replying
If the message is genuinely spam, replying may confirm that your address is actively monitored.
That can sometimes result in even more unwanted messages.
Instead, consider using:
• Your email provider's Report Spam function
• Report Phishing when appropriate
• The sender's legitimate unsubscribe mechanism for legitimate marketing
• The organization's official abuse or security contact
• Appropriate governmental or industry reporting channels
For suspicious messages, preserve the original message and headers before deleting it.
What About an "Unsubscribe" Link?
Not every unsubscribe link should be treated the same way.
For a legitimate newsletter from a company you recognize, an unsubscribe mechanism can be appropriate.
For an obviously fraudulent message, clicking a link can be dangerous.
A malicious link could lead to:
• A phishing website
• Malware
• A fake login page
• Tracking infrastructure
• A page designed to confirm that your address is active
The safest response to an obviously suspicious message is generally to report it rather than interact with its links.
Can You Trace the Individual Person?
Usually, not from the email alone.
This is another common misconception.
Email headers can sometimes identify the mail service, sending server, domain, or intermediary infrastructure.
They do not necessarily reveal the identity or physical location of the individual sitting behind the keyboard.
The apparent originating IP address may belong to a cloud provider, VPN, proxy, corporate gateway, compromised machine, or email service.
Identifying the actual person behind a sophisticated campaign may require information held by service providers and, in appropriate circumstances, legal process.
Why Spam Can Be Difficult to Trace
Modern email delivery is highly distributed.
A single message can travel through several systems:
Sender
?
Email application
?
Marketing/mail service
?
Security gateway
?
Receiving mail server
?
Your mailbox
Each system can potentially add or modify information.
Consequently, tracing an email is often a matter of reconstructing the delivery path rather than finding a single "source address."
A Practical Investigation Workflow
If you receive persistent spam from a no-reply address, a sensible approach is:
1. Preserve the original message
Don't immediately delete it.
2. View the complete headers
Look for From, Reply-To, Return-Path, Received, Authentication-Results, SPF, DKIM, and DMARC information.
3. Identify the apparent organization
Determine whether the message claims to represent a company, service, government agency, or other organization.
4. Verify the organization independently
Do not rely on links or phone numbers contained in a suspicious message.
Use the organization's official website or another trusted source.
5. Determine whether the message is legitimate
If it is legitimate but unwanted, use its official unsubscribe mechanism or report it to the organization.
6. If it appears fraudulent, report it
Use your email provider's phishing/spam reporting mechanism and appropriate authorities or security channels when warranted.
7. Avoid replying to obvious spam
A reply can confirm that your address is monitored and may increase future targeting.
The Bottom Line
A no-reply address is not a magical barrier that makes an email impossible to investigate.
But sending a message directly back to that address is often ineffective.
The more useful approach is to examine the email headers, understand the Reply-To, Return-Path, Received, SPF, DKIM, and DMARC information, and determine which organization or service actually handled the message.
Even then, the infrastructure you discover may be only an intermediary rather than the person who originated the spam.
For legitimate unwanted marketing, use the company's official unsubscribe or contact mechanism. For suspicious or fraudulent messages, avoid interacting with the message and preserve the original information for reporting.
The key lesson is simple:
Don't confuse the address displayed in an email with the complete technical path that delivered it.
Understanding that distinction makes it possible to investigate spam more intelligently—and, in many cases, identify the appropriate organization or abuse channel to which the message should actually be reported.
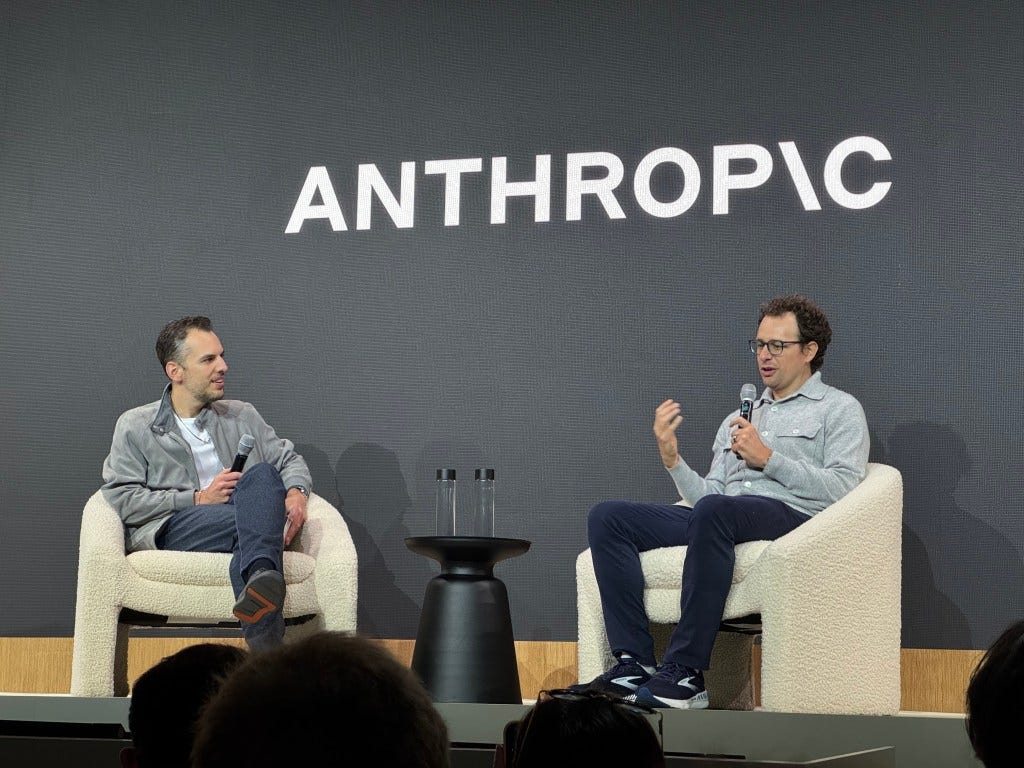
The rise of Anthropic represents one of the most consequential developments in the modern artificial intelligence landscape. Founded in 2021 by siblings Dario Amodei and Daniela Amodei along with a group of former AI researchers and engineers, Anthropic emerged from both optimism and concern about the future of advanced AI systems. Their path to success was shaped not only by technical brilliance but by ethical conviction, institutional friction, fundraising challenges, and a strategic belief that AI must be developed responsibly at scale. The hurdles they faced—and the way they crossed them—help explain why Anthropic is considered a central player in shaping the future of AI.
Origins Inside OpenAI
Before founding Anthropic, many of its core team members worked at OpenAI, one of the world’s leading AI research labs. Dario Amodei served as Vice President of Research, contributing to major breakthroughs in large language models and reinforcement learning systems. The team played critical roles in advancing scaling laws research, which demonstrated that increasing model size and training data often led to predictable improvements in performance.
However, as AI capabilities accelerated, internal debates intensified around governance, commercialization, and safety. The founding team became increasingly focused on alignment—the challenge of ensuring that powerful AI systems behave in accordance with human values and intentions. Concerns about the pace of deployment and long-term safety risks led several key researchers to depart and form a new organization centered explicitly on AI alignment research.
Leaving a high-profile institution was a significant hurdle. OpenAI had brand recognition, financial backing, and momentum. Departing meant forfeiting institutional stability and starting from scratch in a capital-intensive field. Yet the founding team believed that alignment research required deeper structural commitment and independent focus.
Establishing a Safety-First Mission
From its inception, Anthropic positioned itself as a safety-driven AI company. Its core philosophy emphasized “constitutional AI,” a method designed to guide large language models using explicit principles rather than relying solely on human feedback loops. This approach aimed to make models more transparent, controllable, and resistant to harmful outputs.
The hurdle here was conceptual as much as technical. Safety research is often viewed as slower or less commercially attractive compared to product deployment. Convincing investors that alignment-focused development could coexist with business growth required careful framing.
Anthropic’s founders argued that safety is not an obstacle to innovation but a prerequisite for sustainable progress. They believed that increasingly capable AI systems demand increasingly rigorous safeguards. This framing helped differentiate the company in a rapidly expanding AI marketplace.
The Capital Challenge
Training frontier AI models requires immense computational resources. Securing funding for such an endeavor is no small task. Unlike software startups that can operate leanly, AI labs must invest heavily in compute infrastructure, talent acquisition, and research.
Anthropic overcame this hurdle by attracting significant investment from major technology companies and venture capital firms. Strategic partnerships with cloud providers enabled access to large-scale computing resources. These partnerships allowed Anthropic to train its Claude series of AI models, positioning the company as a serious competitor in the generative AI space.
Raising billions of dollars in capital was both a milestone and a challenge. Large investments bring expectations for growth and productization. The founding team had to balance commercial viability with their safety-first ethos. Maintaining alignment as a central mission while scaling operations required disciplined governance structures.
Building Claude and Competing at the Frontier
Anthropic’s flagship AI system, Claude, entered a competitive landscape that included models from OpenAI and other global labs. The hurdle was clear: compete with established players while maintaining a distinct identity.
Anthropic leaned into reliability and safety as competitive advantages. Claude was designed to produce more predictable outputs and demonstrate improved resistance to harmful or biased content. Enterprises seeking AI tools for customer support, research assistance, and knowledge management found value in systems designed with guardrails.
Competing at the frontier also required rapid iteration. AI development cycles are intense, with breakthroughs emerging quickly. The founding team relied on deep expertise in scaling laws and model interpretability research to refine performance. Their scientific grounding enabled them to adapt to evolving benchmarks.
Organizational Culture and Governance
Another major hurdle was organizational design. AI labs face pressure to move fast, release products, and capture market share. At the same time, internal debate about safety, deployment thresholds, and societal impact is essential.
Anthropic adopted a governance structure intended to protect long-term safety goals. It incorporated mechanisms to limit short-term financial pressures from overriding mission commitments. This structure reflects lessons learned from prior experiences in fast-scaling AI organizations.
Balancing idealism with pragmatism remains a constant challenge. As AI systems grow more capable, public scrutiny intensifies. Regulatory discussions around AI transparency, bias mitigation, and risk management continue to evolve. Anthropic’s leadership must engage with policymakers while maintaining technological momentum.
Hurdles in Public Perception
The AI sector is increasingly polarized. Some view advanced AI as transformative and beneficial; others warn of existential risks. Anthropic operates within this tension.
One hurdle is managing expectations. Overhyping AI can erode trust if systems fail to meet promises. Undercommunicating progress risks falling behind competitors in perception. Anthropic has attempted to communicate cautiously, emphasizing incremental improvements and responsible deployment.
Another challenge involves talent competition. Top AI researchers are in high demand globally. Retaining world-class engineers while preserving a mission-driven culture requires both financial incentives and intellectual fulfillment.
Why Anthropic Matters to the AI Future
Anthropic’s significance lies in its integration of safety research with frontier model development. Many organizations focus either on academic safety theory or aggressive commercialization. Anthropic attempts to bridge both.
First, its research into constitutional AI and interpretability contributes to broader understanding of how large language models reason and respond. This work informs industry-wide best practices.
Second, its willingness to scale responsibly demonstrates that safety and capability can advance simultaneously. If successful, this model could influence how other AI companies structure governance.
Third, its partnerships with major cloud and enterprise platforms ensure that its systems are integrated into real-world applications. As AI becomes embedded in business workflows, reliability and controllability become paramount.
Finally, Anthropic’s founding team represents a generation of AI leaders shaped by firsthand exposure to rapid capability growth. Their experiences inside OpenAI gave them insight into both the promise and peril of scaling AI systems. That perspective informs strategic decisions about deployment thresholds and model transparency.
Crossing the Hurdles
The founding team crossed multiple hurdles through:
• Scientific Depth: Leveraging prior research expertise in scaling laws and reinforcement learning.
• Mission Clarity: Anchoring decisions in alignment principles.
• Strategic Fundraising: Securing large investments without abandoning governance safeguards.
• Partnership Building: Collaborating with cloud providers and enterprises.
• Cultural Discipline: Maintaining internal debate and ethical reflection amid growth.
Each phase required balancing ambition with caution. In a field characterized by exponential progress, that balance is difficult but essential.
Conclusion
Anthropic’s founding team transformed concern about AI alignment into an institutional mission. By leaving a leading lab to create a safety-focused frontier company, they embraced uncertainty in pursuit of long-term impact.
Through technical innovation, capital acquisition, and governance design, they positioned Anthropic as a pivotal force in AI development.
As artificial intelligence becomes more powerful and pervasive, organizations capable of combining capability with responsibility will shape its trajectory. Anthropic’s growth reflects both the urgency and the opportunity of this moment. Its founders’ willingness to confront structural hurdles—scientific, financial, and ethical—places the company at the center of debates about how AI should evolve.
In an era when AI systems increasingly influence communication, research, and decision-making, the question is no longer whether AI will shape the future, but how. Anthropic’s founding team has made it clear that safety and alignment must be foundational, not optional. That conviction may prove to be their most important contribution to the AI future.